

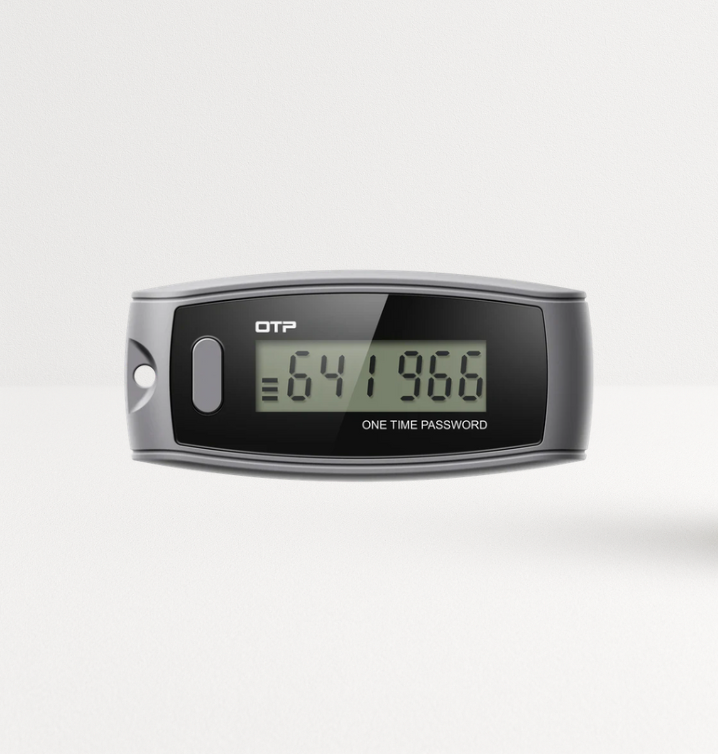
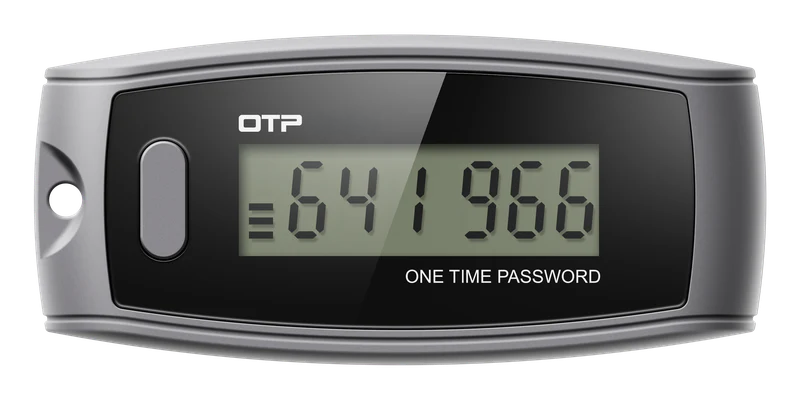

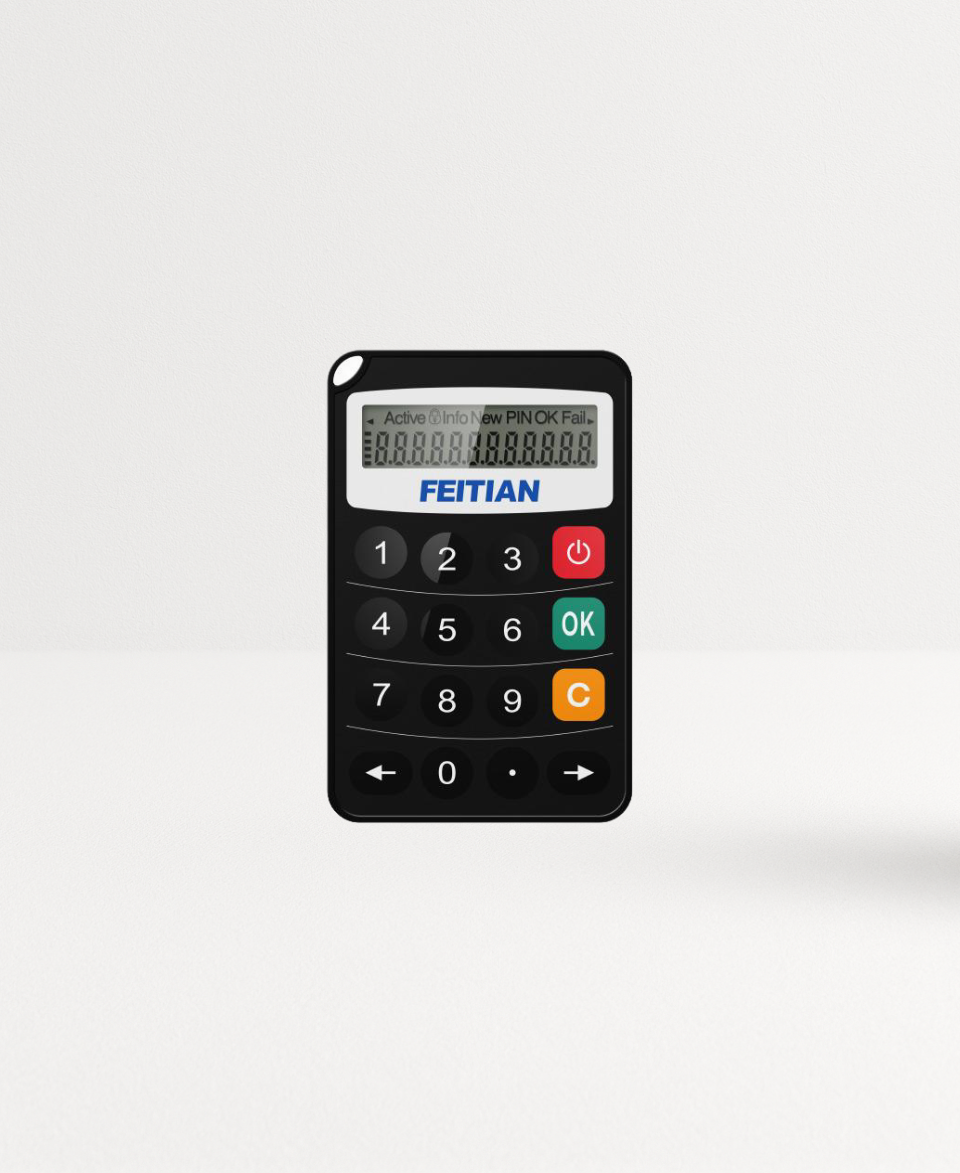
OTP Tokens (One-Time Password Tokens) are secure authentication devices that generate time-based or event-based one-time passwords to verify user identity during login. Ideal for two-factor (2FA) or multi-factor authentication (MFA), OTP tokens provide an extra layer of security for remote access, VPNs, cloud applications, and enterprise systems. These compact, easy-to-use hardware tokens operate independently of network connections and support standard algorithms like TOTP and HOTP, making them compatible with a wide range of authentication platforms, including Microsoft Entra ID, Google Authenticator, and custom RADIUS environments. OTP tokens are perfect for organizations seeking scalable, cost-effective protection against unauthorized access and credential-based attacks.
Time-Based (TOTP) and Event-Based (HOTP) OTP Tokens
FEITIAN OTP tokens follow the open OATH standards and come in two types. Time-based (TOTP) tokens show a new code every 30 or 60 seconds based on the current time. Event-based (HOTP) tokens create a new code each time you press the button, and the code stays valid until it is used. Both types add a second factor to passwords for two-factor (2FA) and multi-factor authentication (MFA).
| Time-based (TOTP) | Event-based (HOTP) | |
|---|---|---|
| How the code changes | Every 30 or 60 seconds | Each button press |
| Code lifetime | Expires after 30 or 60 seconds | Valid until used |
| FEITIAN models | C200 token, VC-200E display card | C100 token, VC-100E display card |
| Works with Microsoft Entra ID | Yes | No |
Compare FEITIAN Hardware OTP Tokens
| Model | Code type | Form factor | Microsoft Entra ID | Also works with |
|---|---|---|---|---|
| C100 | Event-based (HOTP) | Keychain token, I34 casing, IP67 | No | DUO Security, ESET, Entrust, PingID and other HOTP services |
| C200 | Time-based (TOTP), 30 or 60 seconds | Keychain token, I34 casing, IP67 | Yes | Okta, PingID, WatchGuard AuthPoint, SafeNet; not DUO Security |
| C300 | HOTP, TOTP, challenge-response (OCRA), transaction signature | Keypad token with PIN protection | Check your server | Banking transaction confirmation; one token for HOTP and TOTP systems |
| VC-100E | Event-based (HOTP) | Display card, 85.6 x 54 x 0.84 mm | No | DUO Security, ESET, PingID; battery rated above five years |
| VC-200E | Time-based (TOTP), 30 or 60 seconds | Display card, 85.6 x 54 x 0.84 mm | Yes | Okta, PingID, WatchGuard AuthPoint; NFC seed-programming variant |
For a visually impaired user, the C300 Voice speaks its time-based or challenge-response codes and shows them on a large display.
Benefits of OATH-Compliant Hardware OTP Tokens
- No phone needed: a good fit for users who cannot or should not use a smartphone at work.
- Works offline: the token generates codes without a network connection.
- Open standards: OATH TOTP and HOTP work with a wide range of authentication platforms.
- Cost-effective: a simple way to add MFA to remote access, VPNs, cloud applications, and legacy systems that expect a one-time code.
Compatibility and Integration
The time-based C200 works with Microsoft Entra ID, Okta, PingID, WatchGuard AuthPoint, SafeNet Authentication Service, and LinOTP. The event-based C100 and VC-100E are listed as compatible with FEITIAN OTP Authentication Server, Duo Security, ESET Secure Authentication, Entrust Identity Guard, Micro Focus (NetIQ), PingID, and others. The C100 and VC-100E do not work with Microsoft Entra ID, Azure AD, or Azure MFA, so choose the C200 or VC-200E for Microsoft environments. Check each product page for the full compatibility list.
OTP codes can still be typed into a fake site, so for accounts that are common phishing targets, consider FIDO2 security keys. Many FEITIAN FIDO2 keys also support OATH OTP, so one device can cover both.
How to Set Up FEITIAN OTP Tokens in Microsoft Entra ID
Microsoft Entra ID accepts hardware OATH-TOTP tokens with SHA-1 or SHA-256 that refresh every 30 or 60 seconds. It does not support OATH-HOTP, so use the time-based C200 or VC-200E.
- Order time-based tokens. FEITIAN emails the encrypted seed files to the address on the order shortly after shipping, with the password in a separate email. Base32 is the default format for TOTP seeds and the format Entra ID requires.
- Enable hardware OATH tokens in the Entra ID Authentication methods policy.
- Add the tokens to your tenant. Upload the seed file in CSV format under OATH tokens in the Microsoft Entra admin center (Entra ID P1 or P2), or create the tokens with the Microsoft Graph API.
- Assign each token to a user. An administrator assigns it, or with the Graph API method users can self-assign from their Security info page.
- Activate. The user enters the current six-digit code from the token, and Entra ID corrects small clock drift at activation and at every sign-in.
See Microsoft's OATH tokens documentation for the current steps and roles.
Replacing a Proprietary OTP Token System
When a proprietary token contract ends, OATH tokens let you keep hardware codes without tying them to one vendor's server. FEITIAN tokens follow the open OATH TOTP and HOTP standards, so the same tokens work with Microsoft Entra ID, Okta, PingID, DUO Security and the other services on each product page, and you receive the seed files yourself.
- List the systems that ask for a token code today, such as VPN, remote desktop and cloud apps.
- Check which OATH type each authentication server supports: TOTP, HOTP or both.
- Pick the matching model from the table above and the seed format your server imports.
- Pilot with a small group, then issue new tokens in waves and retire the old ones once each group has moved.
Learn More
- Hardware OTP token vs software authenticator: which one fits your users
- How to choose enterprise security hardware
- Best FIDO security keys for MFA
Frequently Asked Questions
What is the difference between TOTP and HOTP tokens?
A TOTP (time-based) token changes its code every 30 or 60 seconds using the current time. An HOTP (event-based) token creates a new code each time you press its button, and that code stays valid until it is used.
Which FEITIAN OTP token works with Microsoft Entra ID?
Use a time-based token such as the C200 or the VC-200E display card. FEITIAN states that the event-based C100 and VC-100E do not work with Microsoft Entra ID, Azure AD, or Azure MFA.
What is the best hardware OTP token for 2FA?
It depends on your authentication server. For Microsoft Entra ID, Okta and PingID, the time-based C200 keychain token or the VC-200E display card fits. For DUO Security and other HOTP services, use the event-based C100 or VC-100E. For banking transactions, the keypad C300 adds challenge-response, transaction signature and PIN protection.
How long do FEITIAN OTP token batteries last?
FEITIAN rates the battery of the VC-100E display card for a life cycle above five years. The C100 and C200 in the I34 casing have extended battery life and a battery-life indicator, so users see when a replacement is due.
How are OTP token seeds delivered?
FEITIAN emails the encrypted seed files to the contact address on the order shortly after shipping, and sends the password in a second email. The default format is Hexadecimal for HOTP and Base32 for TOTP, with PSKC and RFC 6030 XML available on request. Add a note to the order if you need another format or address.
Can I program my own seeds into FEITIAN OTP tokens?
Standard tokens come with seeds set at the factory. The NFC variant of the VC-200E display card can be programmed with your own seed in your facility using an NFC smart card reader or an NFC phone, and the NFC seed programming bundle pairs 10 C200 NFC tokens with an R502-C10 reader for that. NFC is used only for programming, not for sign-in.
Do hardware OTP tokens need a phone or a network connection?
No. The token generates codes on its own, so users do not need a smartphone, and the token itself needs no network connection.